Digital Decoys Multiply to Counter AI Attacks
With AI, offensive operations are gaining speed and scale. The response involves deploying decoys throughout the infrastructure, but their effectiveness hinges on one criterion: appearing real. From Microsoft to Acalvio, including Beelzebub and SentinelOne, the market is organizing around a single idea: transforming the fake into sensors and fake attack paths while lowering production costs.
Indiscernibility: The Success Criterion of Deception
Multiplying decoys brings only limited benefits if automated tools allow attackers to easily distinguish them. The determining factor then becomes the indiscernibility between decoys and real assets. This is assessed on several levels: plausible configurations, coherent histories, realistic identities and permissions, credible interactions between resources, and content compatible with the organization's supposed activities. Artificial intelligence plays a role on both sides: it can help generate more convincing synthetic environments for defenders, but also automate the identification of decoys by attackers.
Industrial Breakthroughs: Acalvio 360 Deception and Generative LLMs
In March 2026, Acalvio launched its 360 Deception strategy, designed to disrupt automated AI attacks. This approach combines the creation of credible fictitious assets and the obfuscation of real assets to complicate the attacker’s mapping of the environment. Meanwhile, the Italian startup Beelzebub claims to use LLMs to simulate Linux servers, API services, and MCP tools, aiming to prolong interaction with the attacker without exposing the real infrastructure. The challenge is not so much to multiply decoys but to reduce their marginal cost of production and maintenance. This movement is part of a broader trend, illustrated by SentinelOne's acquisition of Attivo Networks for $616.5 million to integrate these capabilities into its XDR platform.
Offensive Automation: The Defender's Time is Reduced
According to the UK's National Cyber Security Centre, artificial intelligence is already accelerating reconnaissance phases and vulnerability detection, which reduces the intervention window for defense teams. By early 2026, the most advanced models were capable of executing nearly six times more attack steps than the top-performing models a year and a half earlier. Anthropic reported on a spying operation where agentic AI functions carried out a significant portion of the actions, while laboratories are currently testing their models in offensive contexts equipped with Linux terminals and tools similar to those used by human operators. The main transformation is economic: key tasks are becoming faster and cheaper, shifting the difficulty towards the rapid identification of compromise signals within massive volumes of telemetry. Cyber deception aims precisely to exploit this signal asymmetry.
Le brief IA que les pros lisent chaque soir
Les 7 actus IA du jour, décryptées en 5 min. Gratuit.
Inclus dès l'inscription : notre sélection des meilleurs guides & comparatifs IA.
Choisissez votre rythme
Gratuit · Pas de spam · Désabonnement en 1 clic
From Isolated Traps to Fabricated Attack Paths
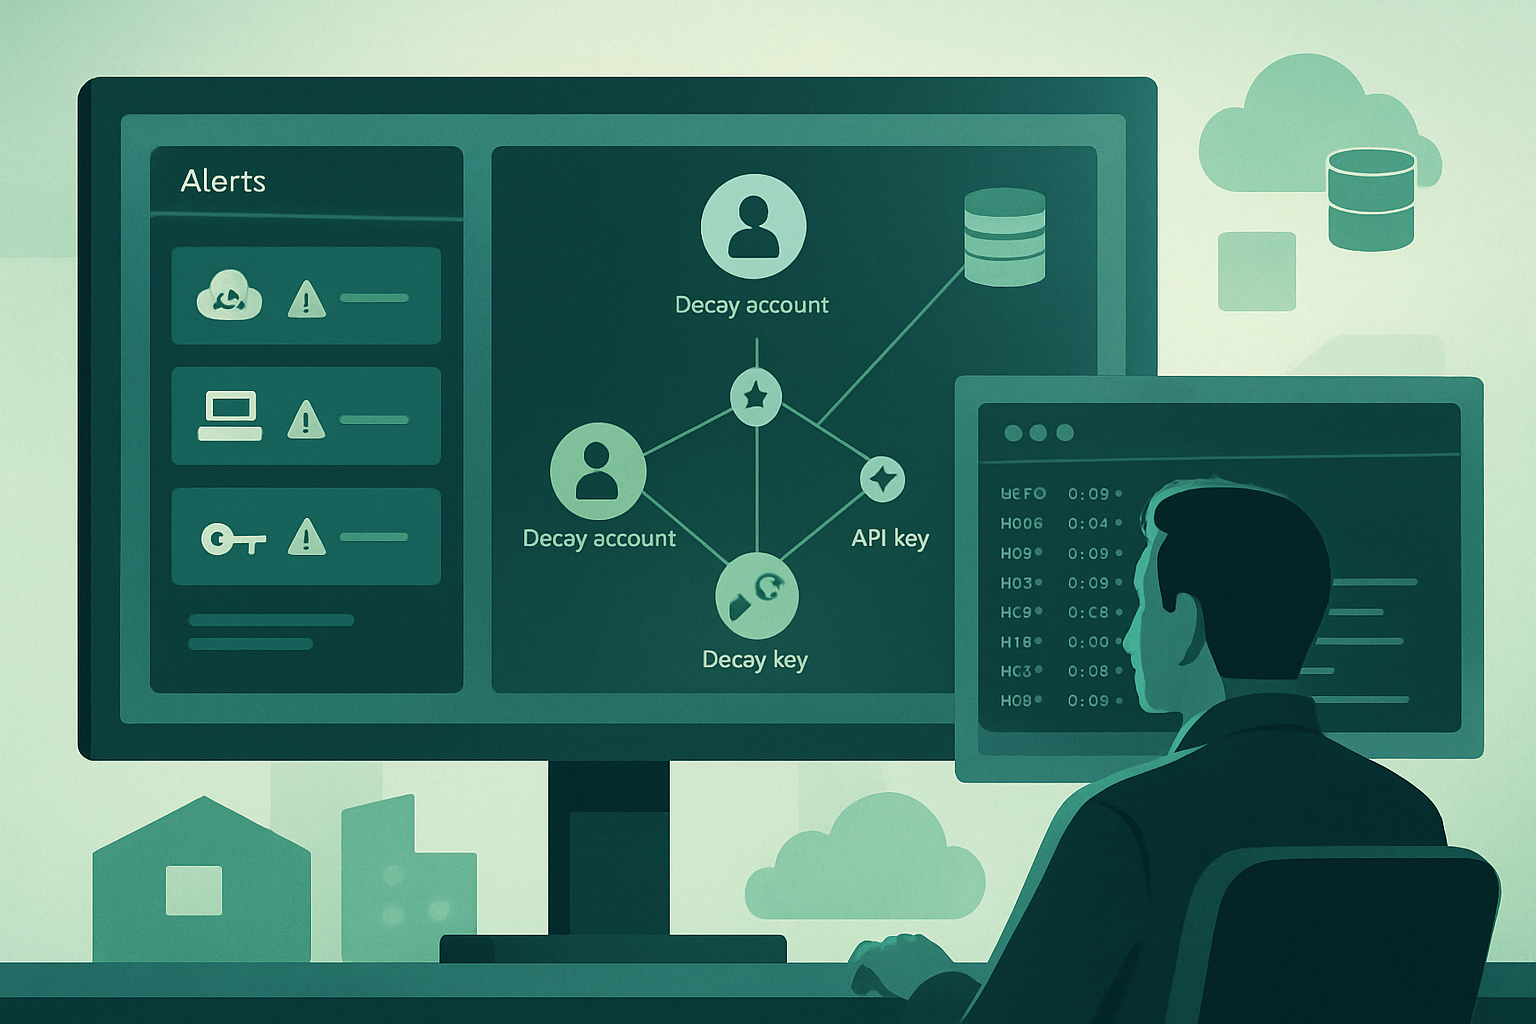
Honeypots, used for decades to lure attackers to fictitious resources, have seen their logic extended to a much larger portion of the information system. Today, security teams are disseminating fake credentials, fictitious administrator accounts, API keys, network shares, cloud tokens, and services with no operational utility. The use of these objects designed as decoys constitutes a signal that is difficult to explain through normal activity. The logic is no longer limited to a single trap: fictitious privileged identities can lead to fake services and secrets, creating an entirely artificial attack path. The fake thus becomes a behavioral sensor, revealing the adversary's intent to exploit it.
Identities and Cloud Become the Main Battleground
In cloud, SaaS, and distributed environments, physical or virtual machines are no longer the sole major target. Identities, IAM rights, tokens, APIs, application secrets, cloud workloads, and machine-to-machine interactions now occupy a central place in the attack surface. Deception is therefore increasingly focused on identity and the cloud, a trend already visible in 2022 when SentinelOne acquired Attivo Networks for $616.5 million to add these features to its XDR platform.
Designing and Maintaining the Fake is Costly
Creating an isolated decoy is relatively simple, but producing thousands of credible ones and maintaining them over time proves complex. A fictitious server whose network traffic, files, user accounts, or information do not reflect the company's environment will be quickly detected. The main cost concerns the need to ensure the consistency and adaptation of the decoy as the real infrastructure evolves: a cloud architecture overhaul, a change in IAM rights, a merger, or an application migration can render some traps obsolete or easily detectable. Several approaches exist, such as using honeytokens that generate alerts in Azure Sentinel, or employing Thinkst's Canarytokens in the form of identifiers, files, or other artifacts. Doctrinally, MITRE Engage reminds us that deception should be designed according to specific defensive objectives and is not limited to a technology to be installed.
Brief IA — L'actualité IA en français
L'essentiel de l'actualité de l'intelligence artificielle, décrypté et expliqué chaque jour.