AI Accelerates Hacking and Vulnerability Discovery
AI Makes Hacking More Accessible, Say Cybersecurity Experts, While the National Vulnerability Database Received Over 10,000 Vulnerability Reports in November. The same tools are used to detect flaws and exploit them. For system administrators, the available time to intervene can be measured in hours.
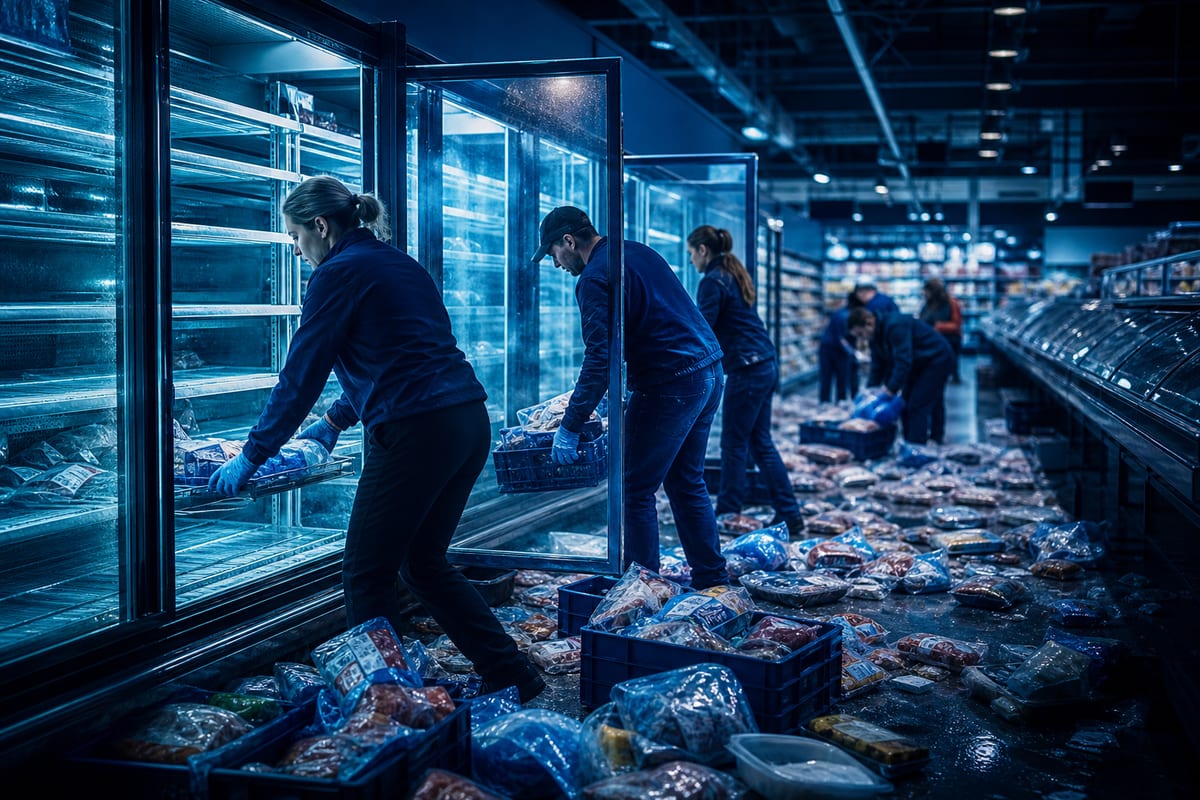
In Sweden, Freezers Reach 50 Degrees
Employees at a Swedish supermarket had to evacuate the contents of freezers after a cyberattack: their temperature had reached 50 degrees Celsius. Among the exposed equipment are also electrical installations and water treatment facilities.
Matt Wyckhouse, CEO of Finite State, a cybersecurity company focused on connected devices, works specifically on refrigerators and smart home equipment. Their software, including the firmware that controls their operation, has undergone less scrutiny than PHP, a widely used language on the Internet. Even without accessible code on GitHub or the Web, a model could reconstruct how a program works and identify a way to attack it.
Such a compromise could render a distributor's food supplies unfit for consumption. Wyckhouse reminds us of society's dependence on the proper functioning of refrigeration. For operators, the difficulty also lies in maintenance: some devices may no longer receive support from the manufacturer, and their managers may be unaware that an update is necessary.
These managers may also lack the skills to repair their systems. In the event of a data breach involving customer information, their liability could be engaged.
Microsoft Fears Hasty Fixes
Satya Nadella, CEO of Microsoft, warned this week at the Dealbook summit that the urgency of fixes would lead to instability. According to him, teams could previously spend a week testing before installing a patch on a critical system. A vulnerability that has already been exploited may now require its installation as soon as it becomes available.
The National Vulnerability Database received over 17,000 CVE reports in October, compared to fewer than 5,000 in October 2025. Wyckhouse attributes the discovery of a significant stockpile of previously unknown vulnerabilities in open-source software to intensive AI analysis.
Previously, the time between discovering a flaw and exploiting it could take several weeks; it can now drop to just a few days or even hours. Companies that write software or operate it are overwhelmed with significant and critical issues requiring rapid intervention. This risk of exploitation contributes to the frequency of updates on computers and their applications.
CrowdStrike Describes Artex-Assisted Attacks
In September and October, intrusions into major South Korean banks led to the theft of personal information. Adam Meyers, Senior Vice President of Counter-Operations at CrowdStrike, indicated that his company suspects a 26-year-old individual located in China and equipped with Artex. According to him, the attacker used AI to prepare for the operation and then to figure out how to sell the data on Telegram. The FBI issued an alert regarding this tool last week.
Le brief IA que les pros lisent chaque soir
Les 7 actus IA du jour, décryptées en 5 min. Gratuit.
Inclus dès l'inscription : notre sélection des meilleurs guides & comparatifs IA.
Choisissez votre rythme
Gratuit · Pas de spam · Désabonnement en 1 clic
Artex falls into the category of harnesses: software that provides a model with instructions and means of action tailored to a task. Claude Code, from Anthropic, and Codex, from OpenAI, rely on this principle for programming. Since the summer, agents have gained autonomy, and attackers' tools have improved.
Cybersecurity experts believe that models released this year have lowered the technical requirements for hacking. Where taking control once required complex, long-acquired expertise just six months ago, some team tasks are now accessible to a 20-year-old equipped with a model and the appropriate program. According to them, an organization no longer needs to be a prestigious or highly lucrative target to attract an attack. Meyers even compares the capabilities now accessible to those of a state.
Developers are trying to limit access to their most powerful models, but offensive capabilities already exist in those available to hackers. Open-weight models can run on their own machines, out of the oversight of providers and authorities. Gary Barlet, Chief Technology Officer for the public sector at Illumio, a specialist in ransomware and intrusions, considers this dissemination irreversible.
Defenders Also Gain Early Access
Anthropic with Project Glasswing, OpenAI with Daybreak, and Google with Fairwind are giving cybersecurity specialists, banks, and healthcare providers early access to their most powerful models. Restrictions on possible research are often relaxed. The PHP vulnerability that prompted an urgent update request from the PHP Foundation in October was discovered thanks to Patch the Planet, a component of Daybreak.
Defensive and offensive tools share their capabilities: scanning sites or code, spotting flaws overlooked by humans, and examining previously under-studied programs at a lower cost. Agents add the ability to act autonomously. The influx of discoveries has been dubbed the "vulnpocalypse."
John Strand, owner and CEO of Black Hills Information Security, tests his clients' protections by reasoning like an attacker. After decades of similar techniques, he predicts a significant advancement in cyber capabilities of models by the end of 2025. According to him, these models effectively identify flaws, while agents automate laborious preparations and deliver results to an operator more quickly.
In October, in front of the business school at Stanford University, Sam Altman, CEO of OpenAI, stated that he no longer believes in the possibility of simply fixing all bugs. He also deemed the attention given to the issue by organizational leaders, countries, and individuals as insufficient.
Recent Outages Without Established Links
Outlook experienced an outage, air traffic control encountered issues, and Chase faced difficulties on Monday. Other incidents involved PHP sites, connected refrigeration equipment, or cryptocurrency holders. No concrete common link has been established between these episodes.
Meyers referred to the previous month as "Black October," and the current month as "Black November," and believes that the situation is not improving. Automated vulnerability searching is coupled with software production: trained on code collected by their designers, models can also generate code. Companies are now having smaller human teams produce more software using AI. The result may contain errors without ever having been checked by a human.
Brief IA — L'actualité IA en français
L'essentiel de l'actualité de l'intelligence artificielle, décrypté et expliqué chaque jour.