Apple Overwhelmed by AI: A $200,000 macOS Flaw Ignored
Le brief IA que les pros lisent chaque soir
Les 7 actus IA du jour, décryptées en 5 min. Gratuit.
Inclus dès l'inscription : notre sélection des meilleurs guides & comparatifs IA.
Choisis ton rythme
Gratuit · Pas de spam · Désabonnement en 1 clic
An Overwhelmed Reward Program
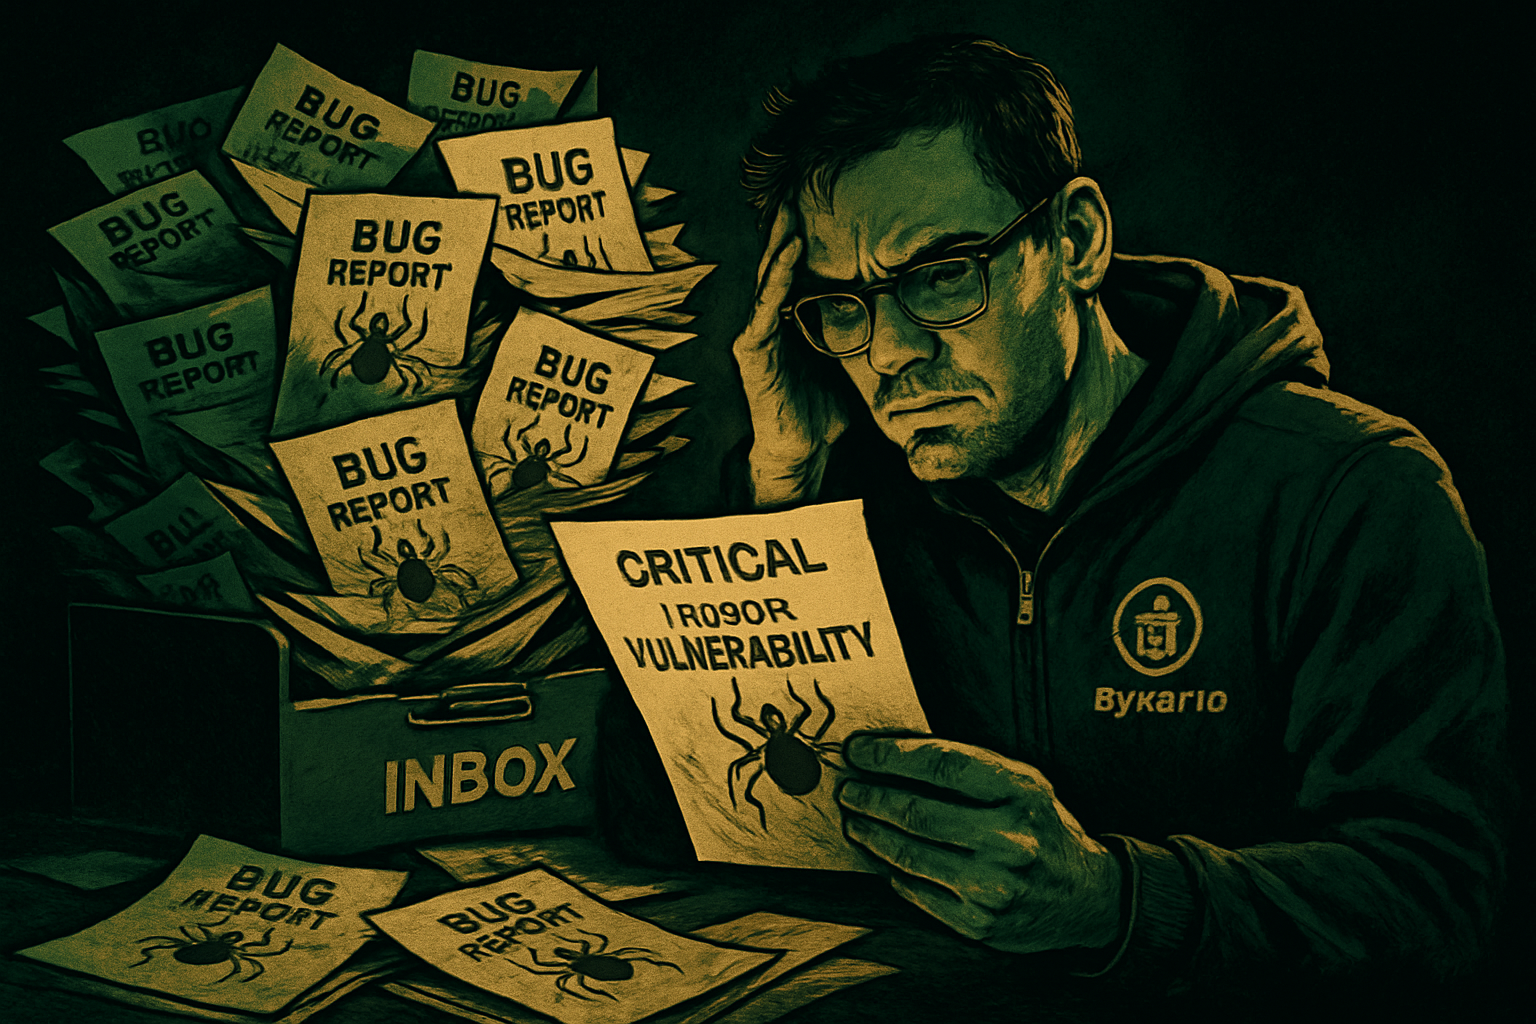
Apple's bug bounty program, designed to encourage the discovery of vulnerabilities, is currently facing an unexpected issue. It is overwhelmed by an avalanche of bug reports generated by artificial intelligence. This situation has prompted Apple to limit the number of submissions allowed per researcher in order to manage the verification of reports more effectively.
A Critical Flaw Left Unreported
This saturation has had notable consequences. The Italian cybersecurity startup Bynario was unable to report a critical flaw in macOS. This vulnerability, if exploited, could have been worth up to $200,000 on the black market. The inability to report this flaw highlights the challenges posed by the increasing use of AI in generating bug reports.
Implications for Security
The current situation raises questions about the effectiveness of bug bounty programs, especially when automated tools flood communication channels. The failure to detect such significant vulnerabilities could have serious repercussions for the security of macOS users.
Brief IA — L'actualité IA en français
L'essentiel de l'actualité de l'intelligence artificielle, décrypté et expliqué chaque jour.