ChatGPT: HTML Preview Vulnerability Fixed, $5,000 Reward
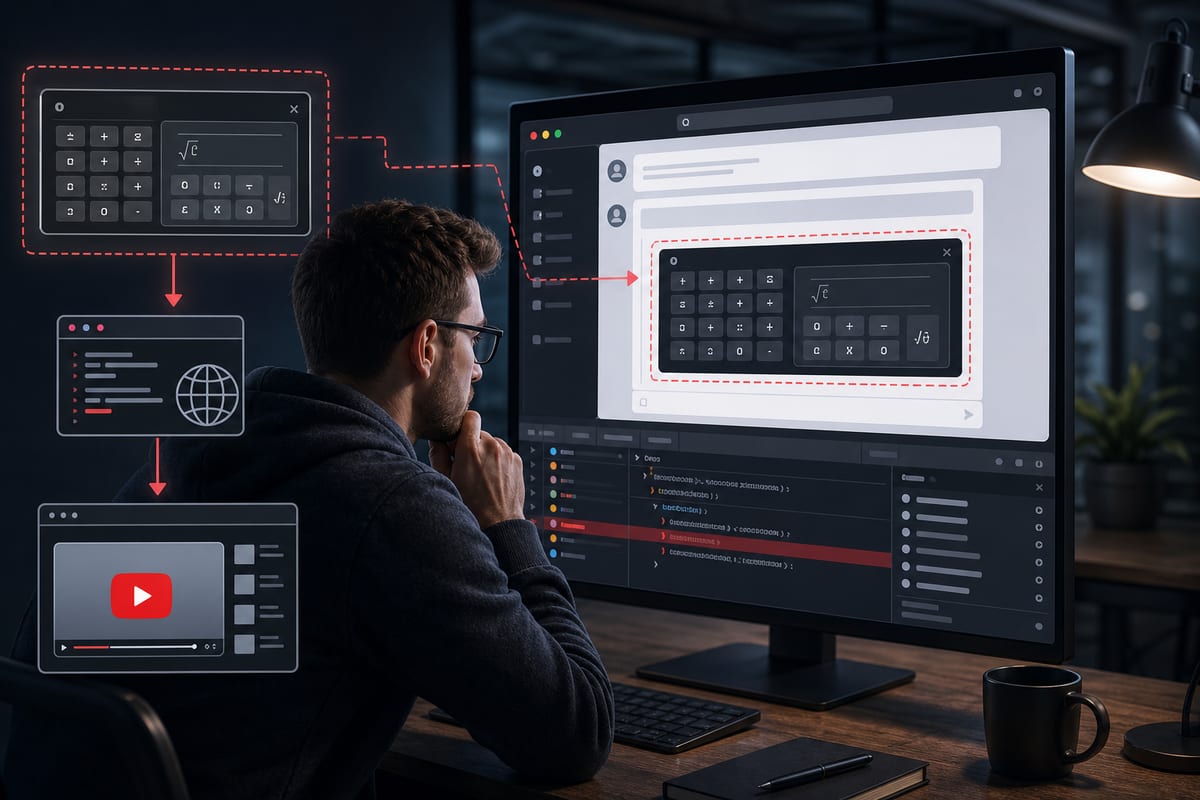
A vulnerability in the HTML preview management of ChatGPT allowed for the execution of JavaScript and the retrieval of private user data via a simple share URL. OpenAI has patched the flaw and awarded $5,000 to Parameter Labs, which considers the reward modest given the severity of the bug. The attack notably exploited MathLive and a bypass via YouTube's oEmbed despite a restrictive CSP policy.
OpenAI fixes code execution and pays $5,000
OpenAI has addressed the reported vulnerability in ChatGPT. Parameter Labs, the discoverer of the issue, received a reward of $5,000. Before the fix, exploiting the flaw allowed for the execution of JavaScript in ChatGPT, making it possible to retrieve private user data via APIs and exfiltrate it using an image reference. A ChatGPT share URL could, if opened by a logged-in user, enable the exfiltration of their data or the execution of actions on their behalf. Parameter Labs believes that the awarded bounty is low considering the severity of the vulnerability.
Attack chain: MathLive, postMessage, innerHTML, and YouTube
The vulnerability exploited the MathLive JavaScript library, which OpenAI uses for graphical management. MathLive provides a virtual keyboard that can be activated in the parent page using postMessage() sent from a sandboxed iframe. The code responsible for processing these messages used innerHTML, allowing the sender to insert custom HTML into the parent page, without a mechanism to prevent other sandboxed iframes, including those from HTML previews, from exploiting this feature. Even though innerHTML does not directly execute scripts, it could be used to inject a new iframe without sandbox restrictions. OpenAI's CSP policy prohibited inline scripts and limited external scripts to a few domains, including YouTube. The YouTube oEmbed endpoint could then be used to return executable JavaScript, enabling code execution on the ChatGPT page.
Le brief IA que les pros lisent chaque soir
Les 7 actus IA du jour, décryptées en 5 min. Gratuit.
Inclus dès l'inscription : notre sélection des meilleurs guides & comparatifs IA.
Choisissez votre rythme
Gratuit · Pas de spam · Désabonnement en 1 clic
Targeted function and role of the HTML preview sandbox
The attack targeted the implementation of HTML previews in ChatGPT, a feature that displays interactive HTML applications in a sandboxed iframe. This feature, previously known as Canvas, is referred to in its latest version as HTML previews. The sandbox of the iframes aims to prevent untrusted code from interacting with OpenAI's APIs or accessing private data. Parameter Labs discovered an exploitation chain that allowed for bypassing this isolation.
Brief IA — L'actualité IA en français
L'essentiel de l'actualité de l'intelligence artificielle, décrypté et expliqué chaque jour.