Unit 42 Details an Automated AI Attack from China
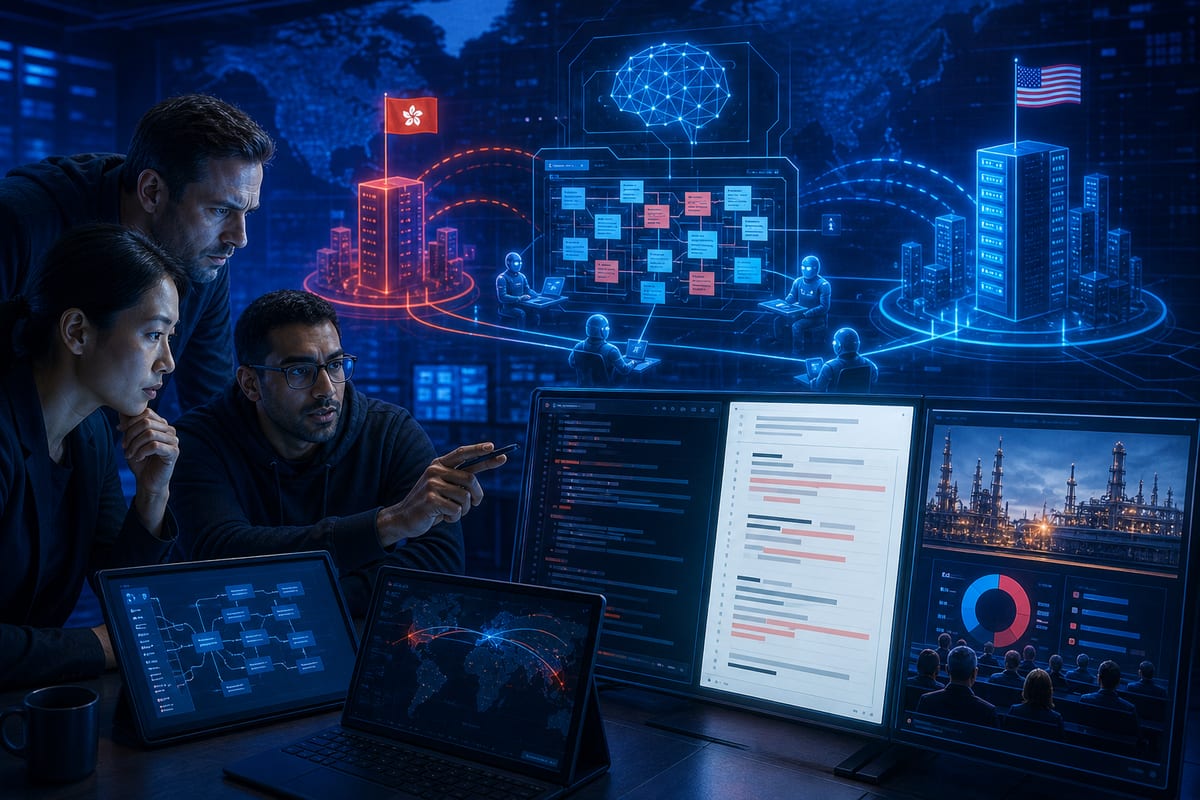
Palo Alto Networks Unit 42 describes an automated intrusion campaign relying on the open-source framework Cairn and Chinese models Zhipu GLM and DeepSeek. Monitored in August and September 2026, it led to unauthorized access, data capture, and manipulation of an industrial bulletin. The observed method, based on a "blackboard" and authorization tricks, fuels expert alerts about the achievable scale and obsolescence of certain defense models.
Neutralized Safeguards and a Distributed Attack Chain from Hong Kong to the U.S.
Cairn's work prompts instruct the model to never refuse a task. Operators reinforced this directive with an authorization pretext, generating an authorization.md file for each operation claiming that the action was authorized, equating the creation of the task to a commitment approved by a client. Each task was initiated with the root domain of the target to allow the framework to autonomously enumerate the attack surface. Execution relied on a customized fork of Cairn operated from a server in Hong Kong, with a staging and output node hosted in the United States. Individual operations varied from 20 minutes to over 50 hours, with no time constraints imposed by the attackers.
Observed Intrusions: Cloud Storage, Admin Accounts, and Altered Voting Bulletin
Unit 42 reports unauthorized access to a cloud storage space as well as the modification of a live bulletin associated with an industrial standardization vote. By exploiting various vulnerabilities, the attackers were able to impersonate any clients, allowing them to gain read, write, and delete permissions on meeting, voting, and back-office management features. Several product systems saw the addition of persistent admin accounts. In one company, over a million records were exfiltrated, while in others, military and government identities were compromised. Chinese-speaking individuals gained unauthorized access to 10 targeted companies and dozens of valid credentials. These activities were observed in August and September 2026.
Le brief IA que les pros lisent chaque soir
Les 7 actus IA du jour, décryptées en 5 min. Gratuit.
Inclus dès l'inscription : notre sélection des meilleurs guides & comparatifs IA.
Choisissez votre rythme
Gratuit · Pas de spam · Désabonnement en 1 clic
Automation by Cairn: 3 to 7-Step Plans and Model-Agnostic Framework
Coordination took place through a shared blackboard: agents read and wrote a graph of facts and intentions, while human operators could inject hints at any time. Confirmed discoveries accumulated as immutable facts, and the agent prepared its next actions as intentions. For each target, the model developed a distinct plan of three to seven steps. The framework is agnostic to model choice, and operations were conducted with Zhipu GLM 5.2 and DeepSeek V4 Flash/Pro. The attackers had previously armed Cairn by pairing it with these Chinese AI models.
Scope of the Campaign and Alerts: Scale, Attribution, and Resilience
In total, Unit 42 tracked 25 operations targeting at least 19 organizations. The team estimates that a single person or a small group managed the entire operation, hitting 19 organizations in two weeks, with operations sometimes exceeding 50 hours. For Andy Piazza, the attack illustrates a feared scale: the campaign can interact with 1,000 organizations in parallel, prompting a shift away from perimeter risk models and significantly complicating attribution and fingerprinting. Justin Greis emphasizes that AI now coordinates the intrusion, selecting the suite based on results and reducing manual effort, which alters the economics of targeting: pressure can be maintained on more targets without managing each step, and risk can grow without a change in vulnerability. He recommends that CISOs monitor unauthorized changes to critical records and privileged access, and test their ability to verify and restore reliable information post-incident, with resilience including trust in steering data. Frank Dickson considers the campaign "impressive in the worst sense," praises the tracking method (blackboard, facts, intentions, prompts), and notes that traditionally costly work is shifting to "API billing line." He estimates that AI attack agents have moved from unsuccessful trials to actual breaches in about three months.
Brief IA — L'actualité IA en français
L'essentiel de l'actualité de l'intelligence artificielle, décrypté et expliqué chaque jour.